用 Twitch 登录
要为你的项目启用 Twitch 认证,你需要先创建一个 Twitch 应用,然后把应用的 OAuth 凭证添加到你的 Supabase 仪表板里。
🌐 To enable Twitch Auth for your project, you need to set up a Twitch Application and add the Application OAuth credentials to your Supabase Dashboard.
概览 #
🌐 Overview
为你的应用设置 Twitch 登录由三部分组成:
🌐 Setting up Twitch sign-in for your application consists of 3 parts:
- 创建并配置一个 Twitch 应用 Twitch 开发者控制台
- 将你的 Twitch OAuth 消费者密钥添加到你的 Supabase 项目
- 将登录验证码添加到你的 Supabase JS 客户端应用
访问你的 Twitch 开发者账号 #
🌐 Access your Twitch Developer account
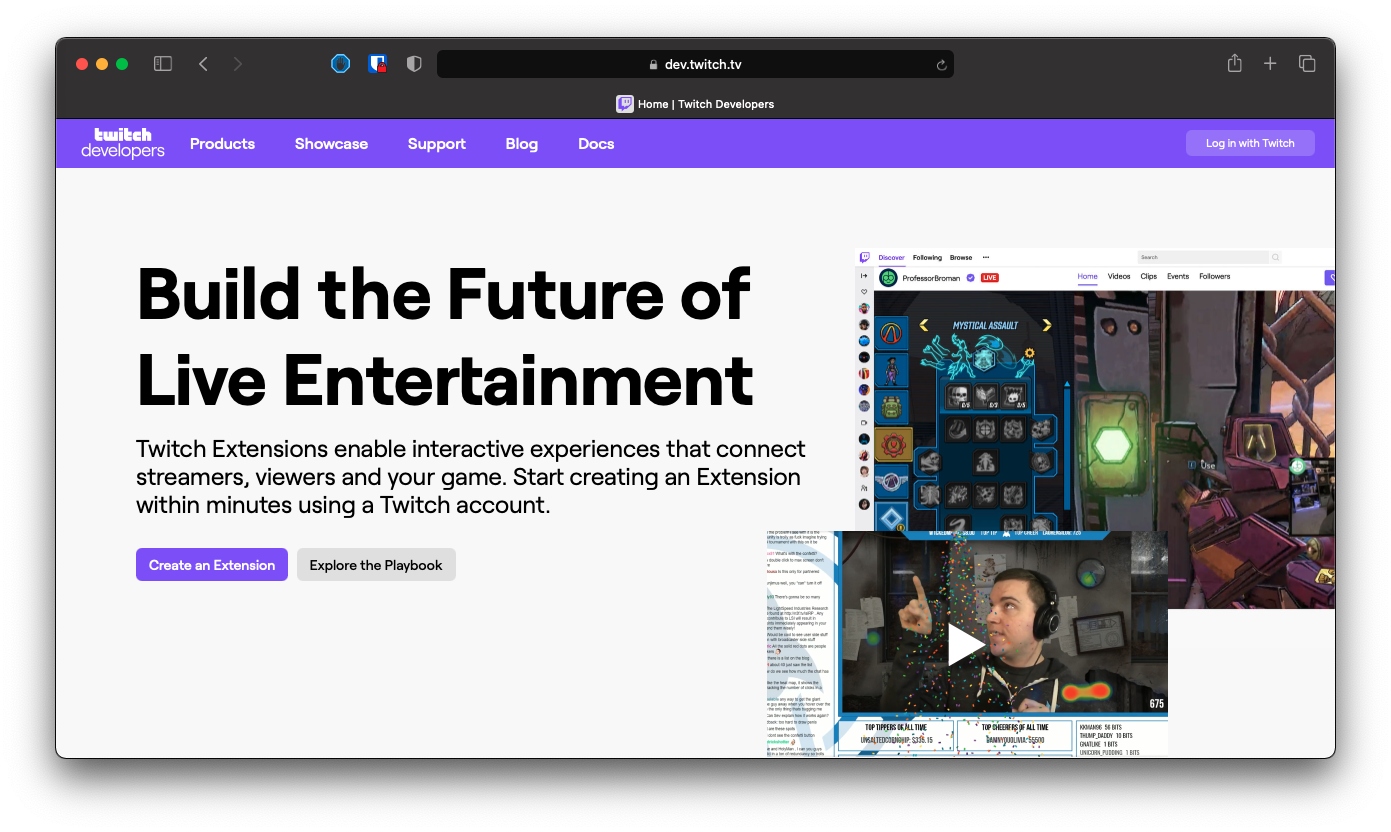
- 去 dev.twitch.tv。
- 点击右上角的
Log in with Twitch登录。 - 如果你还没有为你的 Twitch 账号启用两步验证,你需要先在 Twitch 安全设置 启用它,然后才能继续。
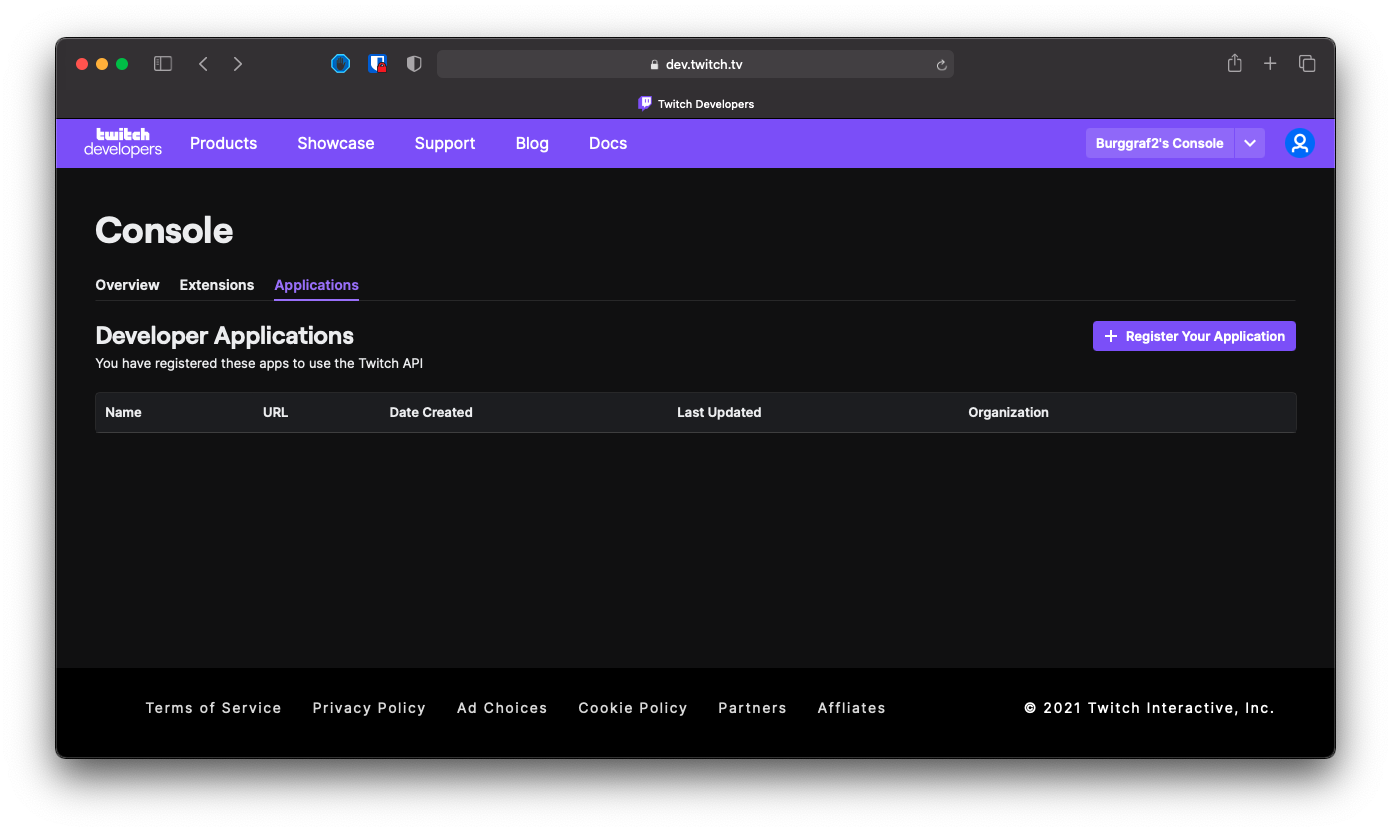
- 登录后,前往 Twitch 开发者控制台。
找到你的回调网址 #
🌐 Find your callback URL
下一步需要一个回调 URL,看起来像这样:https://<project-ref>.supabase.co/auth/v1/callback
- 前往你的 Supabase 项目仪表板
- 点击左侧边栏的
Authentication图标 - 在配置部分点击
Sign In / Providers - 点击手风琴列表中的 Twitch 展开,你就会找到你的 回调 URL,你可以点击
Copy将其复制到剪贴板
本地开发 #
🌐 Local development
在本地使用 Supabase CLI 测试 OAuth 时,确保你的 OAuth 提供商已配置本地 Supabase Auth 回调 URL:
🌐 When testing OAuth locally with the Supabase CLI, ensure your OAuth provider is configured with the local Supabase Auth callback URL:
http://localhost:54321/auth/v1/callback
如果这个回调 URL 缺失或配置错误,OAuth 登录可能会失败,或者在本地开发时无法正确跳转。
🌐 If this callback URL is missing or misconfigured, OAuth sign-in may fail or not redirect correctly during local development.
有关更多详情,请查看本地开发文档。
🌐 See the local development docs for more details.
要在本地使用 Supabase CLI 测试 OAuth,请参阅本地开发文档。
🌐 For testing OAuth locally with the Supabase CLI see the local development docs.
创建一个Twitch应用 #
🌐 Create a Twitch application
- 点击右上角的
+ Register Your Application。
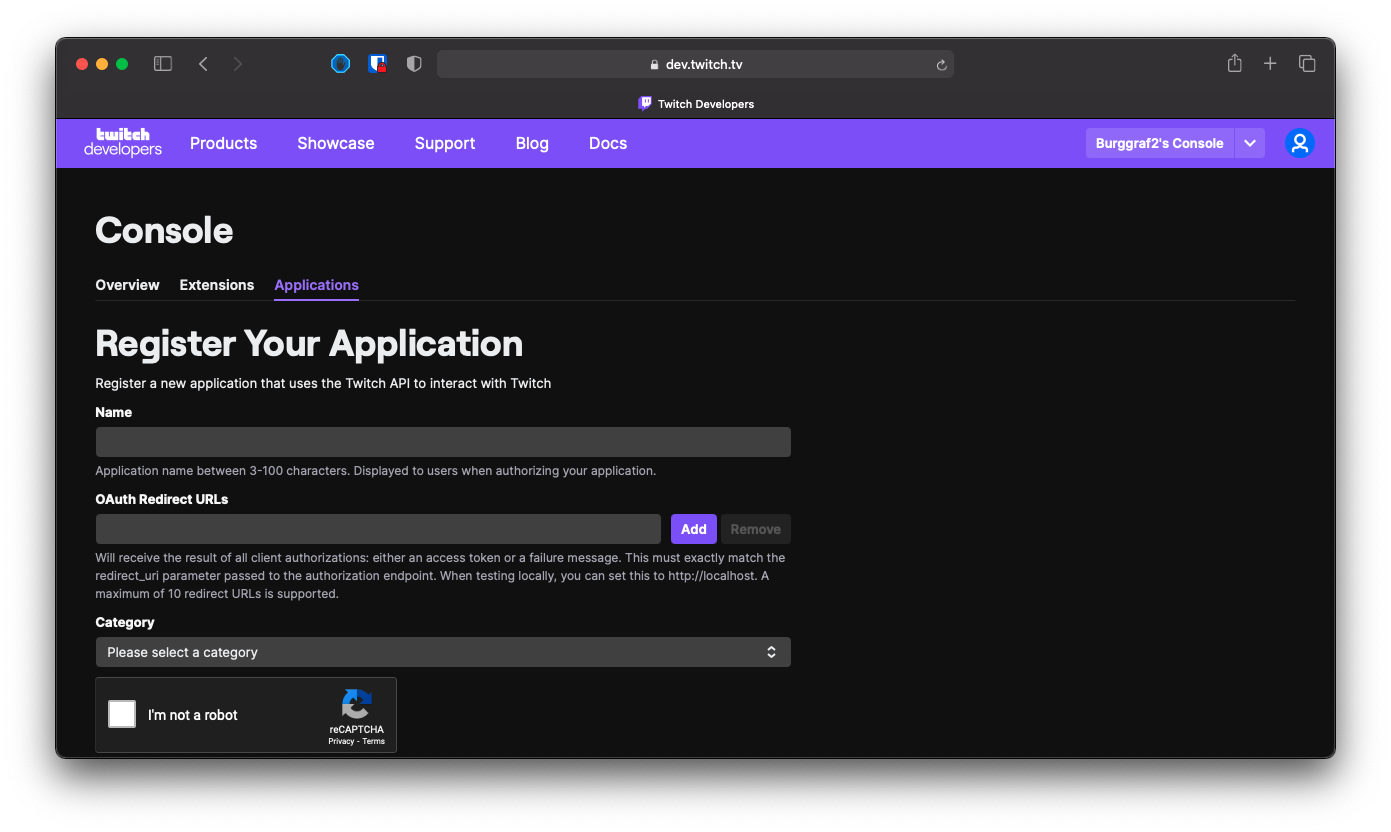
- 输入你的应用名称。
- 输入或粘贴你的
OAuth Redirect URL(上一步的回调 URL)。 - 为你的应用选择一个类别。
- 勾选验证码框,然后点击
Create。
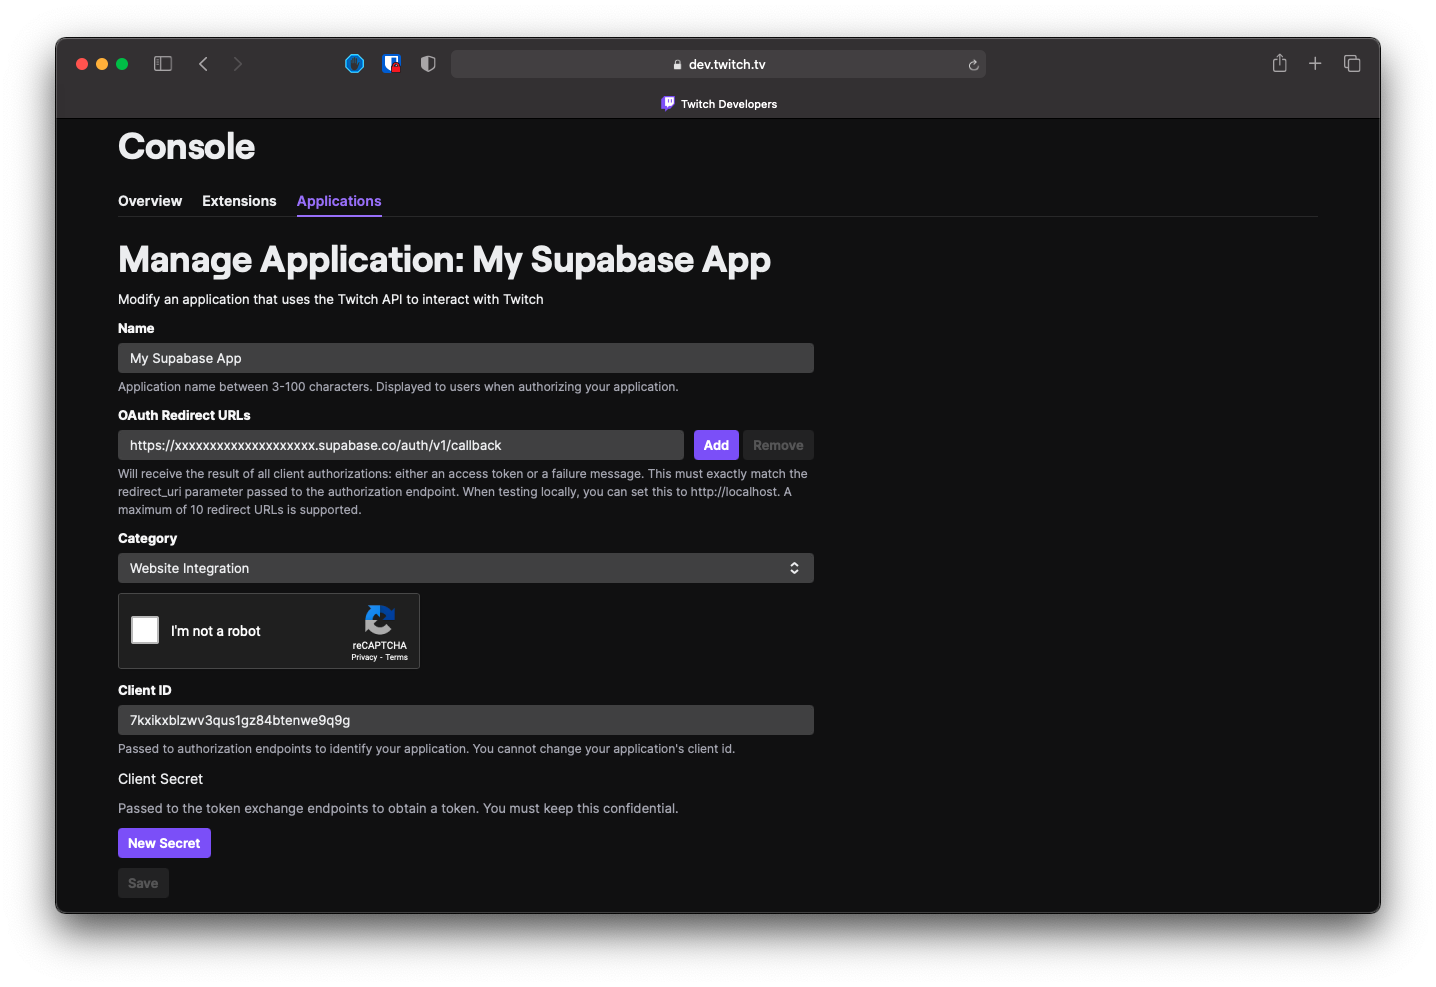
获取你的 Twitch OAuth 客户端 ID 和客户端密钥 #
🌐 Retrieve your Twitch OAuth client ID and client secret
- 点击列表中你应用条目右侧的
Manage。
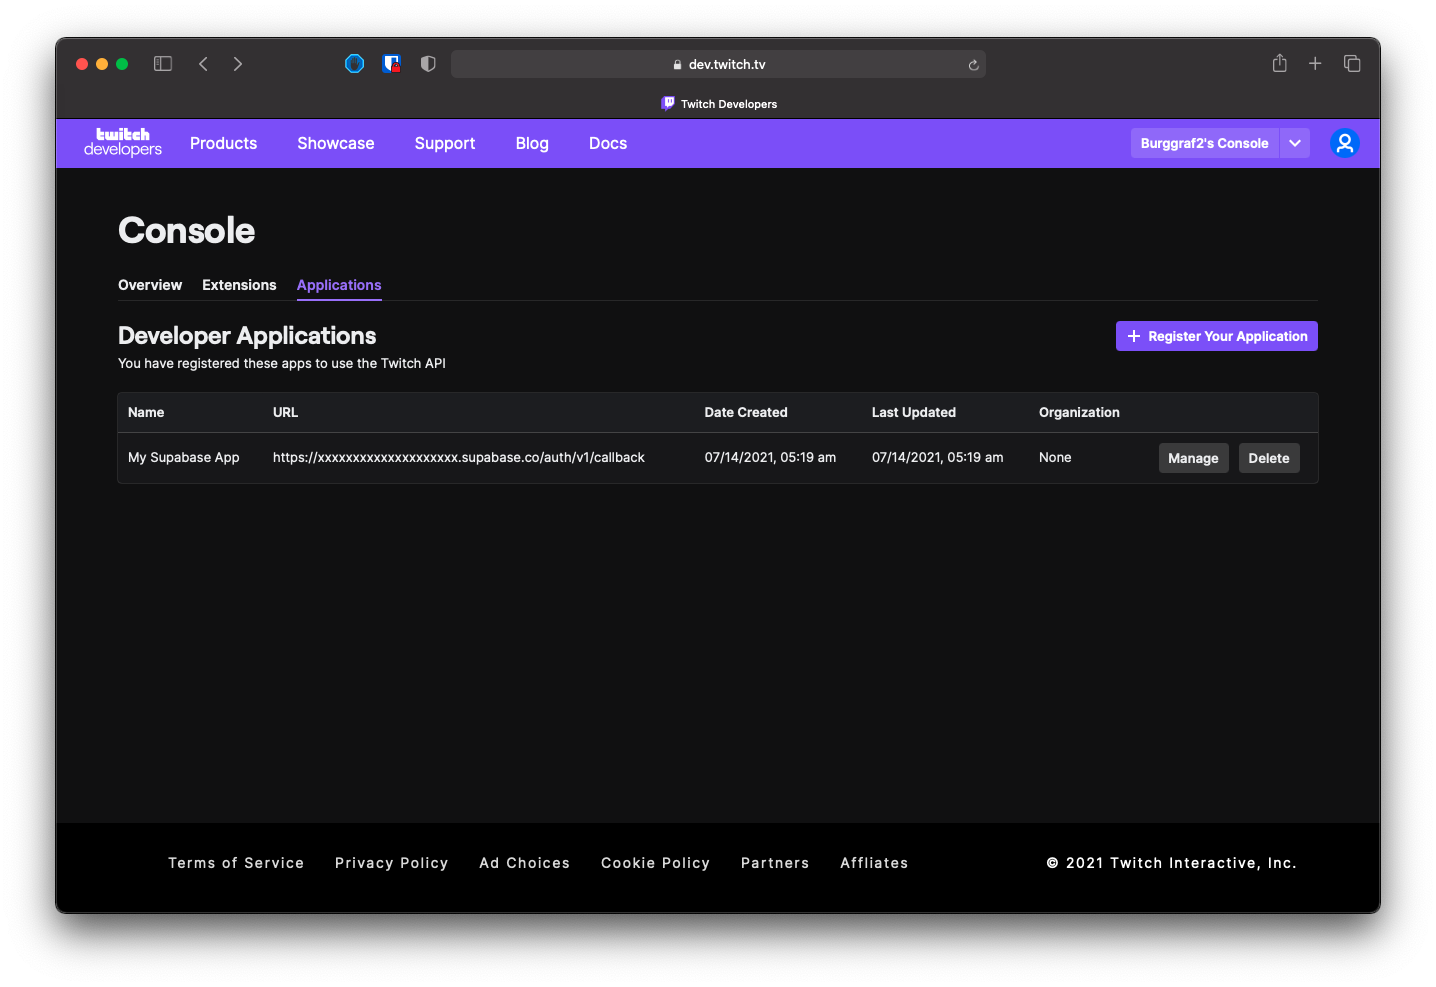
- 复制你的客户端ID。
- 点击
New Secret来创建一个新的客户端密钥。 - 复制你的客户端密钥。
在你的 Supabase 项目中添加 Twitch 凭证 #
🌐 Add your Twitch credentials into your Supabase project
- 前往你的 Supabase 项目仪表板
- 在左侧边栏,点击
Authentication图标(靠近顶部) - 在配置部分点击
Providers - 从手风琴列表中点击 Twitch 来展开,然后将 Twitch 启用 切换为开启
- 输入你在上一步保存的 Twitch 客户端 ID 和 Twitch 客户端密钥
- 点击
Save
在你的客户端应用中添加登录代码 #
🌐 Add sign-in code to your client app
确保你在以下代码中使用了正确的 supabase 客户端。
🌐 Make sure you're using the right supabase client in the following code.
如果你没有使用服务器端渲染或基于 Cookie 的认证,你可以直接从 @supabase/supabase-js 使用 createClient。如果你在使用服务器端渲染,请查看 服务器端认证指南 获取创建 Supabase 客户端的说明。
🌐 If you're not using Server-Side Rendering or cookie-based Auth, you can directly use the createClient from @supabase/supabase-js. If you're using Server-Side Rendering, see the Server-Side Auth guide for instructions on creating your Supabase client.
当你的用户登录时,用 twitch 作为 provider 调用 signInWithOAuth() :
🌐 When your user signs in, call signInWithOAuth() with twitch as the provider:
async function () { const { , } = await ..({ : 'twitch', })}以 PKCE 流程为例,比如在服务端认证中,你需要一个额外的步骤来处理代码交换。在调用 signInWithOAuth 时,提供一个指向回调路由的 redirectTo URL。这个重定向 URL 应该添加到你的 重定向允许列表 中。
🌐 For a PKCE flow, for example in Server-Side Auth, you need an extra step to handle the code exchange. When calling signInWithOAuth, provide a redirectTo URL which points to a callback route. This redirect URL should be added to your redirect allow list.
在浏览器中,signInWithOAuth 会自动重定向到 OAuth 提供商的认证端点,然后再重定向到你的端点。
🌐 In the browser, signInWithOAuth automatically redirects to the OAuth provider's authentication endpoint, which then redirects to your endpoint.
await ..({ , : { : `http://example.com/auth/callback`, },})在回调端点,处理代码交换以保存用户会话。
🌐 At the callback endpoint, handle the code exchange to save the user session.
在 app/auth/callback/route.ts 创建一个新文件,并填入以下内容:
🌐 Create a new file at app/auth/callback/route.ts and populate with the following:
import { NextResponse } from 'next/server'// The client you created from the Server-Side Auth instructionsimport { createClient } from '@/utils/supabase/server'export async function GET(request: Request) { const { searchParams, origin } = new URL(request.url) const code = searchParams.get('code') // if "next" is in param, use it as the redirect URL let next = searchParams.get('next') ?? '/' if (!next.startsWith('/')) { // if "next" is not a relative URL, use the default next = '/' } if (code) { const supabase = await createClient() const { error } = await supabase.auth.exchangeCodeForSession(code) if (!error) { const forwardedHost = request.headers.get('x-forwarded-host') // original origin before load balancer const isLocalEnv = process.env.NODE_ENV === 'development' if (isLocalEnv) { // we can be sure that there is no load balancer in between, so no need to watch for X-Forwarded-Host return NextResponse.redirect(`${origin}${next}`) } else if (forwardedHost) { return NextResponse.redirect(`https://${forwardedHost}${next}`) } else { return NextResponse.redirect(`${origin}${next}`) } } } // return the user to an error page with instructions return NextResponse.redirect(`${origin}/auth/auth-code-error`)}资源 #
🌐 Resources